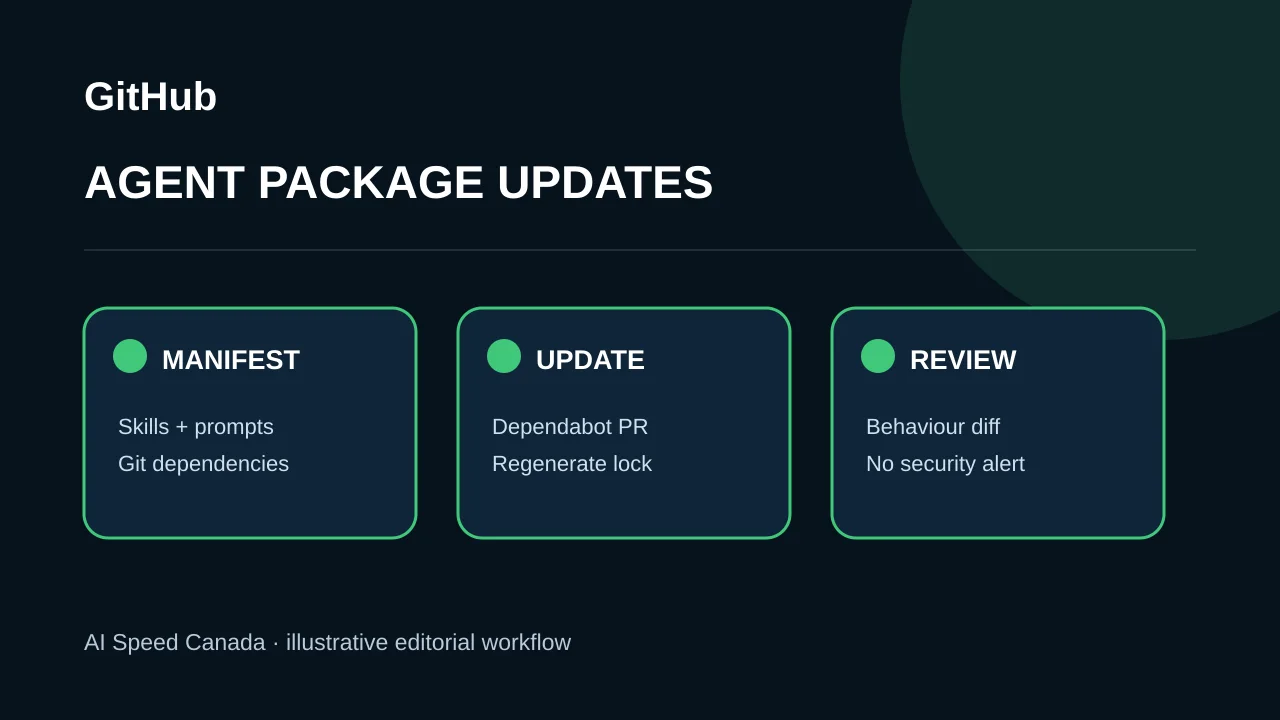
GitHub added generally available Dependabot version-update support for Agent Package Manager on November 3, 2026. APM packages can contain AI-agent skills, prompts and instructions. Dependabot can open pull requests for supported Git dependencies declared in apm.yml and regenerate apm.lock.yaml when the lockfile is present. GitHub explicitly says this support covers version updates, not security updates.
The setup follows Dependabot’s scheduled-update model
Repository maintainers add an apm ecosystem entry to .github/dependabot.yml, point it at the directory containing apm.yml and choose an update schedule. The feature is available on github.com across GitHub plans, with GitHub Enterprise Server 3.24 named as the future server release.
A successful configuration means Dependabot can propose supported changes. It does not mean every dependency type or reference is covered. Teams should compare the generated lockfile with the manifest and confirm which repository, revision and transitive content will actually be used.
Related sources: GitHub: Dependabot version updates support Agent Package Manager ↗
Updating instructions can change agent behaviour without changing application code
A skill or prompt package can influence tool choice, file edits and decision rules. A version bump may therefore alter operational behaviour even when no compiled dependency changes. Review the source diff, provenance and requested capabilities before merging.
Treat agent packages as executable influence in the supply chain. Pin dependencies where reproducibility matters, require review from the workflow owner and test the updated package on a representative task. A regenerated lockfile improves traceability only if the runtime actually honours it.
Related sources: GitHub: Dependabot version updates support Agent Package Manager ↗
Version automation is not vulnerability detection
GitHub’s release note is unambiguous that APM security updates are not included. Dependabot will not turn this configuration into an alerting system for malicious instructions, leaked data, prompt injection or unsafe tool permissions.
Teams need separate controls: trusted sources, commit review, content scanning where useful, least-privilege tools and a rollback path. A package being current can reduce drift while still introducing an unwanted behavioural change. “Latest” and “safe” are different properties.
Related sources: GitHub: Dependabot version updates support Agent Package Manager ↗
Start with one low-risk agent workflow and measure update friction
Canadian teams can pilot a repository that handles no production credentials or personal information. Record the previous package versions, expected agent output, review time, test results and any newly requested access.
Success is not merely an automatically opened pull request. It is an update that is understandable, reproducible and verified without expanding permissions silently. Watch for documentation on supported dependency forms, Enterprise Server delivery and any future security-update coverage.
Sources and editorial method
We use the linked original statements and reports to distinguish documented facts from our analysis. Company announcements describe their authors’ plans and claims; they are not independent verification of future outcomes. This article is dated and will be revised if material evidence changes. Read our editorial standards and corrections process.
- GitHub: Dependabot version updates support Agent Package Manager ↗ — Official November 3 release; supported update behavior, configuration, availability and explicit security-update exclusion.